Who is Compliflo for?
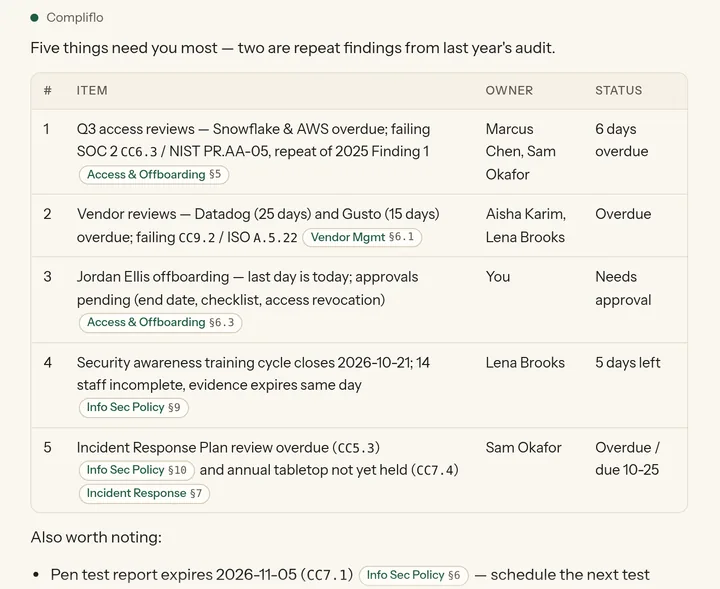
Small and mid-sized companies working toward or maintaining SOC 2, ISO 27001, HIPAA (Security Rule) or NIST CSF, usually where one person looks after compliance alongside another job.
What do I need to start?
The documents you already have: policies, procedures, past audit reports and evidence, as PDF, Word, Markdown or text files (or a zip of them) up to 10 MB each. You can upload many at once and review Compliflo’s suggested types and control mappings before saving. Scanned PDFs need text recognition first.
Does it replace our auditor, or our judgment?
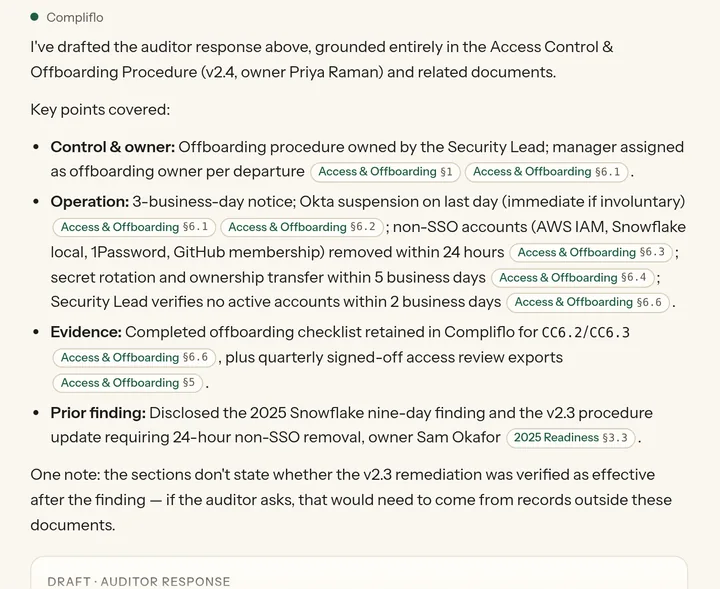
No. It reads, drafts and keeps track. People approve every change, and your auditor still does the audit. Compliflo makes the evidence easier to find and explain.
What happens when my documents don’t cover something?
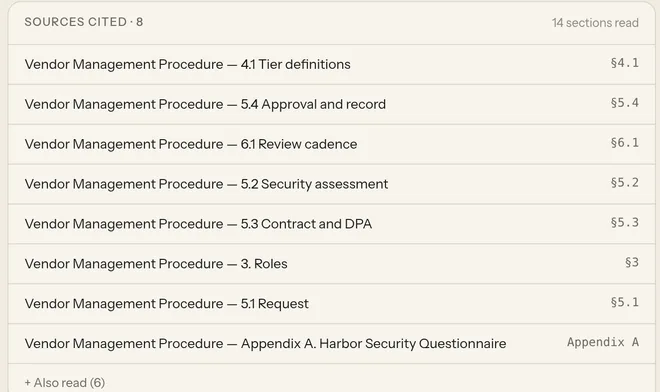
It tells you so, and points to the closest sections it did find.
Will it send emails on its own?
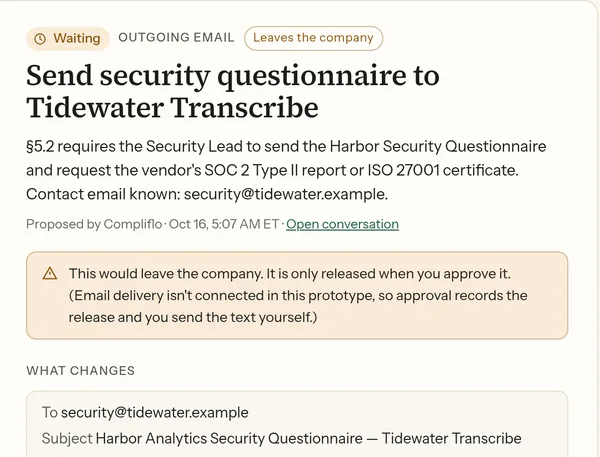
No. Outgoing messages always wait for a person. Today, approving one records the release and gives you the text to send yourself; sending from Compliflo is coming later.
Can my team use it?
Yes. The workspace owner invites teammates by email; each invitation link works once and expires after 7 days. Owners can invite and remove people, approvers can approve or reject what Compliflo proposes, and members can ask, upload and propose but not approve. Every invitation, acceptance and removal is in the audit log.
Is our data used to train AI models?
No. We never use your documents, prompts or answers to train models, and our AI provider is contractually barred from training on or keeping your prompts.
Is Compliflo open to everyone yet?
Not yet. The beta starts on November 10 and is invite-only while we bring teams on a few at a time. It is free during the beta. Request an invite and we will reply from the beta team. The demo is open to anyone. Pricing has the notice we will give before that changes.
Can I try it without uploading anything?
Yes. The demo is Harbor Analytics, a fictional 60-person company with its policies, vendors, people, systems and controls already loaded. You can reset it to the start at any time.
Can we store patient health information?
Not yet. Compliflo helps you map your policies to the HIPAA Security Rule, but please don’t upload patient health information (PHI): we don’t sign Business Associate Agreements (BAAs) yet.
What isn’t built yet?
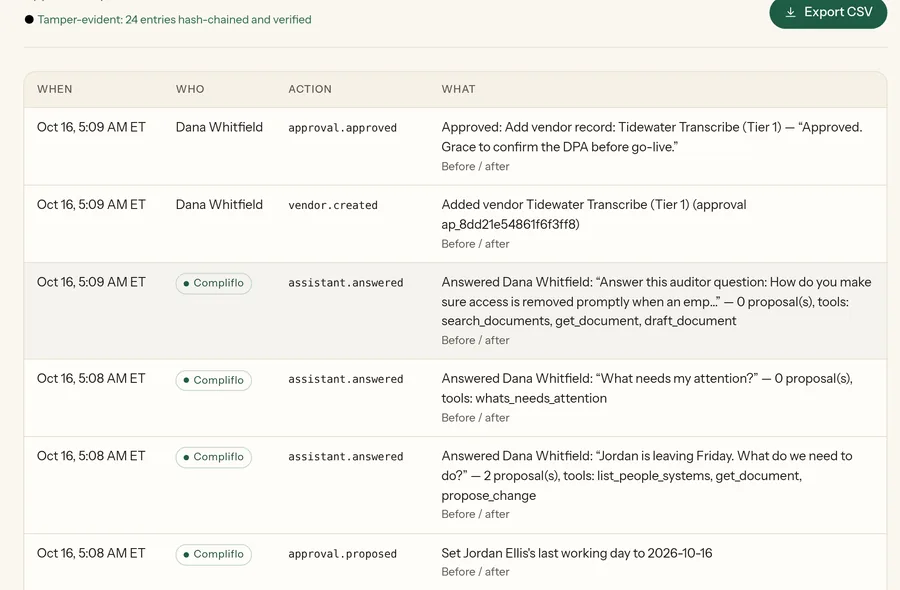
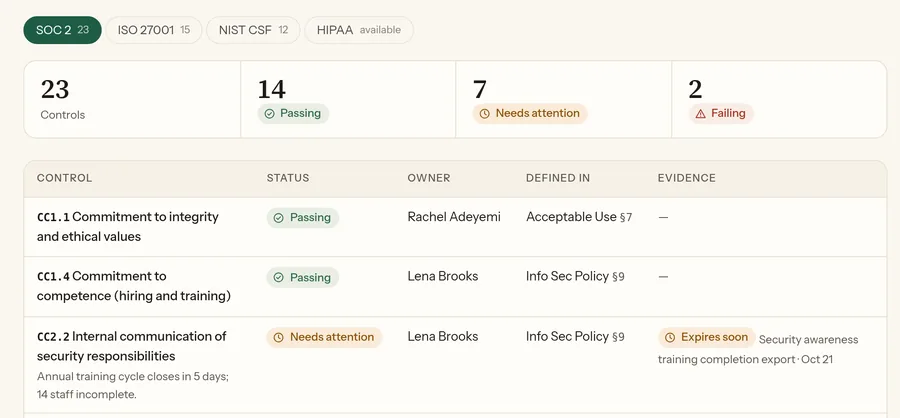
A daily digest email, a calendar of due dates and staff policy attestations are on the way. Bulk upload with classification review, HIPAA Security Rule and NIST CSF 2.0 catalogs, the audit log CSV export and a full workspace export (ZIP) work today. The SOC 2 and ISO 27001 catalogs are starter sets today, not the full lists. Compliflo helps you prepare for SOC 2 and ISO 27001; Compliflo itself isn’t SOC 2 audited yet.